Focal Point logo

Put your team under pressure.

Every instructor has field experience in adversary emulation, threat hunting or SOC operations, including training SOC personnel across NATO countries. Whichever programme you choose, your team works hands-on in controlled simulation environments, against realistic attacker behaviour.

40+

Organisations trained across EU, USA and Asia

1,300+

Cyber defenders engaged

5

Sector specific cyber ranges

60+

Blue and purple team labs

220+

Hours of specialist learning content

A readiness journey, one step at a time

Each programme is a stage of CRORE, our Cyber Resilience and Operational Readiness Ecosystem, taking your team from a first baseline to validated, sector-specific readiness. Every programme is delivered 100% remotely. Start at the stage that matches your team's maturity.

Cyber Defence Experience programme badge
012 days

Cyber Defence Experience

First engagement

A practical entry point. Your team works a realistic intrusion scenario end to end, investigating attacker activity through SIEM telemetry as it unfolds in a live environment.

Who it is for

  • Organisations running an operational cyber defence exercise for the first time
  • Mixed-seniority teams that need a shared baseline
  • Organisations that want a pilot before committing to a longer programme

What your team leaves with

  • A shared baseline experience across the team
  • An attack timeline your team reconstructs itself
  • A purple-team report accounting for the full attack chain

Cyber Tactical GameOptional add-on
Defender Blue programme badge
025 days

Defender Blue

Defensive focus

Investigation, detection thinking and response readiness through SIEM-led workflows, delivered in an environment built for your own industry.

Who it is for

  • SOC analysts, incident responders and detection engineers
  • Blue teams looking to validate their process
  • Organisations improving investigation maturity and workflow consistency

What your team leaves with

  • Detection rules developed and validated during the cycle
  • Alert triage, threat hunting and incident investigation practised under pressure
  • A team capstone: one campaign, one shared narrative, presented

Cyber Tactical GameIntegrated session

Defender Purple programme badge
035 days

Defender Purple

Validation loop

Attacker execution and defensive investigation worked as one loop. Delivery is sector-specific: execution and detection validation are carried out against sector systems and operational dependencies rather than a generic enterprise network.

Who it is for

  • Mature SOC teams ready to validate detection coverage
  • Teams improving their purple-teaming practices and workflows
  • Organisations that want to test their SOC against a realistic adversary

What your team leaves with

  • Detection gap analysis and validation cycles
  • Red and blue workflow alignment
  • Lifecycle-based purple-teaming workflows your SOC applies day to day

Cyber Tactical GameIntegrated session

Tailored Operational Readiness Validation programme badge
045 days, extensible

Tailored Operational Readiness Validation

Highest fidelity

We build a simulation environment around your own infrastructure and threat model, then challenge selected critical operations through realistic scenarios and provide evidence to inform improvement. It combines the adversarial depth of Defender Purple with the flexibility to weight delivery towards blue team investigation, sector-specific scenarios, or both. Scope and approach are agreed privately.

Who it is for

  • Organisations that need evidence a critical service can continue during an attack
  • Organisations that have experienced cyber incidents and need to build validated response capability
  • Clients seeking simulation aligned to their own infrastructure and operational environment

What your team leaves with

  • A simulation environment, scenarios and evaluation criteria built around your critical operations
  • Evidence of where operations hold and where they break
  • Repeatable validation as your systems and threats change

Cyber Tactical GameOptional add-on
CRORE Complete badge

Your readiness journey continues.

From initial cyber defence capability to tailored operational validation, each engagement strengthens resilience and builds the evidence needed to inform continuous improvement.

Earn CRORE Complete through any of our operational validation exercises: Defender Blue, Defender Purple or Tailored Operational Readiness Validation. Threats change every year, and so do our exercises. Return each year to keep your readiness, and your CRORE Complete, up to date.

  • Defender Blue
  • Defender Purple
  • Tailored Operational Readiness Validation

Evidence in a language a regulator already reads

Exercises are aligned to NIS2, the EU directive covering essential and important entities, and mapped to MITRE ATT&CK, the knowledge base of adversary tactics and techniques. Findings therefore travel to a board, an auditor, a ministry or another supplier without translation.

NIS2 aligned

Continuity of essential services, demonstrated rather than asserted.

MITRE ATT&CK mapped

Adversary behaviour described in the vocabulary your auditors and suppliers already use.

The Cyber Tactical Game

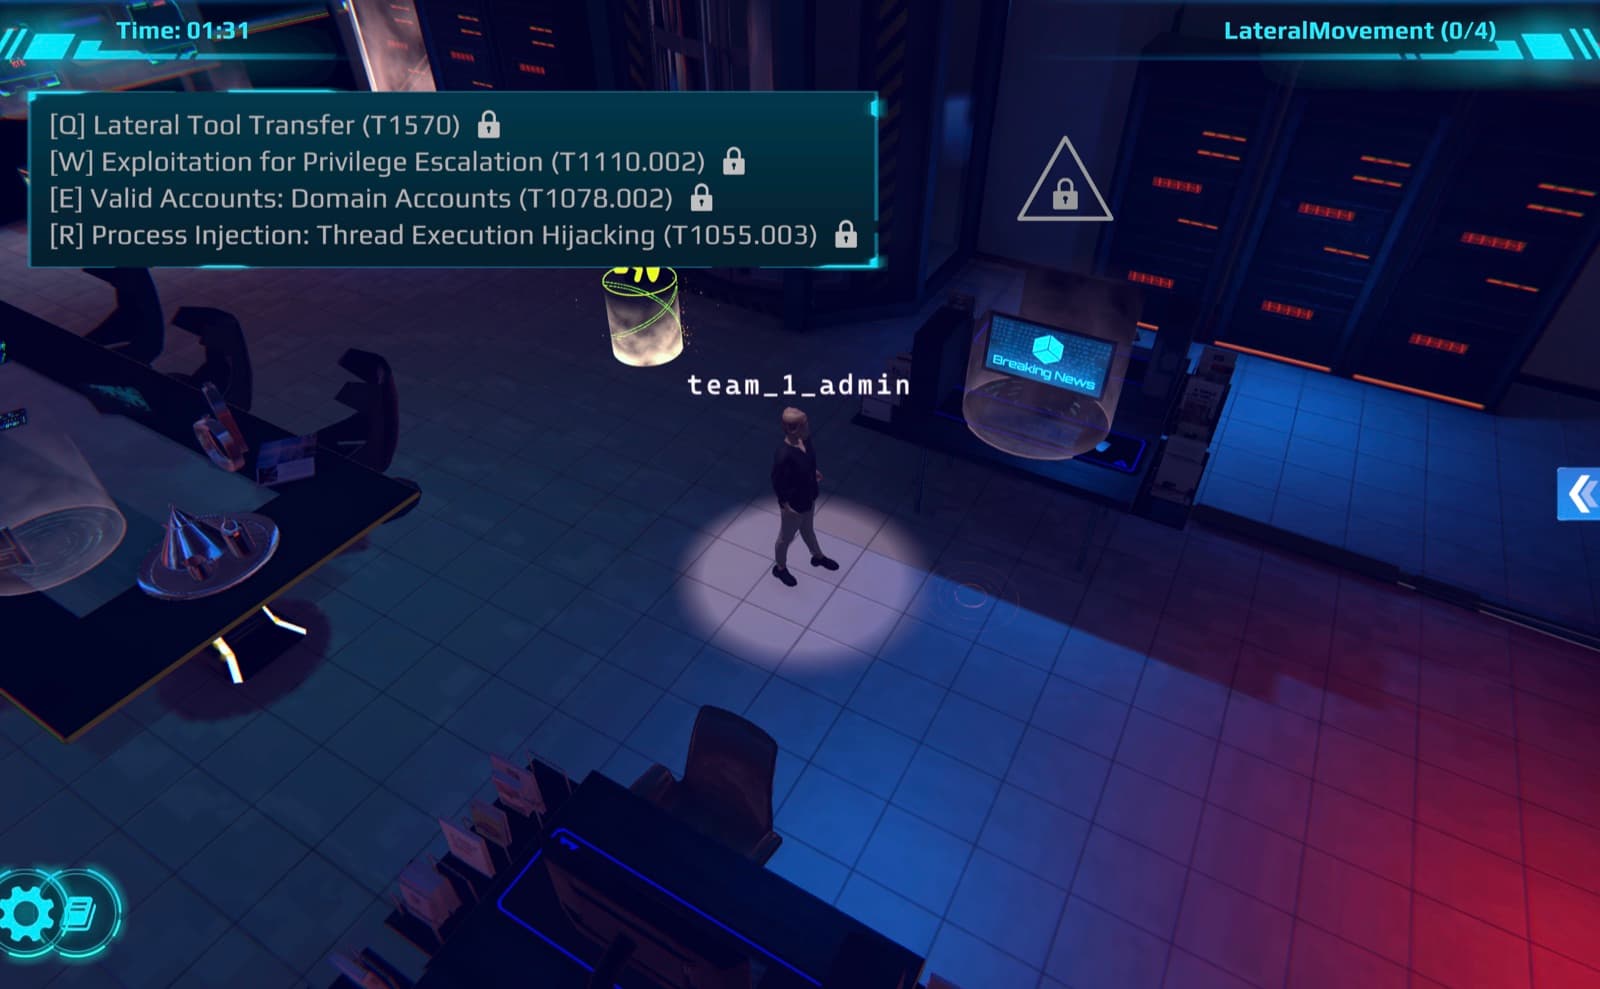
Time-pressured incident simulation in an immersive environment. Practice team coordination, awareness of cyber defence practices and critical thinking throughout the phases of an incident. Each scenario is built to mirror the technical exercise environment and provide a collaborative context to test learner's skills in communication and defensive response.

Cyber Defence Experience
Optional add-on, subject to engagement planning
Defender Blue
Integrated session
Defender Purple
Integrated session
Tailored Operational Readiness Validation
Optional add-on
The Cyber Tactical Game: a team member moving through a data centre with MITRE ATT&CK techniques available as timed actions.

Our instructors

Senior professionals with frontline experience in incident response, red teaming, adversary emulation and detection engineering across security organisations and military environments.

Red teamers

Adversary-led expertise

Offensive security specialists with 10+ years of experience each, the most senior over 20. They work across exploit development, penetration testing, adversary emulation, malware analysis and threat intelligence, with deep roots in critical infrastructure. They know how real intrusions unfold because they run them.

Blue teamers

Detection & response expertise

Defenders with 10+ years of experience each, from incident response leads to cloud security architects. They specialise in SIEM detection engineering in Microsoft Sentinel, endpoint security with Microsoft Defender, cloud security, threat hunting, forensic investigations and the delivery of red versus blue exercises in critical infrastructure.

GIAC

  • GPEN

    GIAC Penetration Tester

  • GXPN

    GIAC Exploit Researcher and Advanced Penetration Tester

  • GCPN

    GIAC Cloud Penetration Tester

  • GCFA

    GIAC Certified Forensic Analyst

Zero-Point Security

  • CRTO

    Certified Red Team Operator

  • CRTL

    Certified Red Team Lead

ISC2

  • CISSP

    Certified Information Systems Security Professional

OffSec

  • OSCP

    OffSec Certified Professional

EC-Council

  • CEH Master

    Certified Ethical Hacker Master

Microsoft

  • Azure Security Engineer

    Microsoft Certified: Azure Security Engineer Associate

Red Hat

  • RHCSA

    Red Hat Certified System Administrator

What must keep operating?

Tell us about the critical function or operational challenge that matters most. We'll explore how its resilience and readiness can be challenged and demonstrated.